
Status: CURRENT — COMMUNITY OIDC / PRE-STABLE PLUGIN
Last reviewed: 31 August 2026
Applies to: Jellyfin + Authentik using the community SSO/OIDC pluginImportant: Authentik’s current official Jellyfin integration guide now recommends LDAP, not OIDC. This article is specifically for people who still want OIDC/SSO through the community Jellyfin SSO plugin.
⚠️ Keep a break-glass Jellyfin admin account. A bad role mapping can remove administrator permissions from the account you normally use. Before changing SSO/admin-role settings, create or keep a second local Jellyfin administrator that does not depend on OIDC.
A quick 2026 update
When I originally wrote this article, the common OIDC option was the 9p4/jellyfin-plugin-sso plugin. That repository was archived by its author on 12 May 2026.
There is now a community revival maintained under Flowfin/jellyfin-plugin-sso. It supports Authentik over OpenID Connect and retains role-based mappings including administrator roles. It also keeps the same plugin GUID as the original 9p4 plugin, so it is designed to install over an existing installation while keeping the configuration.
At the time of this review the Flowfin project is still pre-stable/release-candidate software, so read its current installation notes before using it on a production Jellyfin server.
If you just want the Authentik-supported path with fewer moving parts, the current Authentik Jellyfin guide uses Jellyfin’s LDAP Authentication plugin instead.
The admin-role problem
With the OIDC SSO plugin, Jellyfin can use a role/group claim from Authentik to decide whether an SSO user should have Jellyfin administrator permissions.
The important settings are:
- Role Claim: usually
groupswhen using Authentik’s group claim. - Admin Roles: the exact Authentik group name that should grant Jellyfin administrator access.
For example, I originally used Authentik’s default administrator group:
authentik AdminsYou can also create a dedicated group specifically for Jellyfin administrators, which is cleaner than tying Jellyfin permissions to Authentik’s own superuser/admin group.
In Authentik go to:
Admin Interface → Directory → Groups → CreateCreate something like:
jellyfin-adminsAdd only the users who should have Jellyfin administrator access to that group, then configure the Jellyfin SSO plugin with:
Role Claim: groups
Admin Roles: jellyfin-adminsThe group name needs to match the value Authentik actually sends in the groups claim.
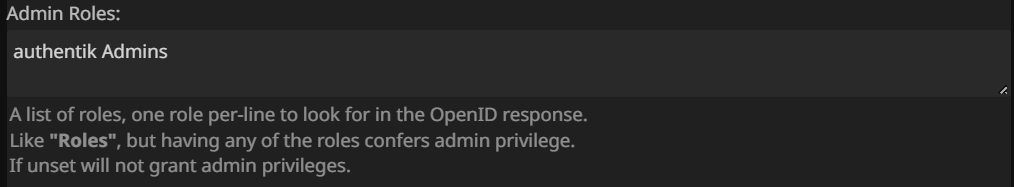
I also resized this screenshot from the original article because WordPress was rendering the full-size image way too large and making it look stretched.
Why admin access can disappear
The SSO plugin uses the role/group information supplied by the identity provider to determine administrator status. If your configured Admin Roles do not match anything in the incoming role claim, the SSO login may no longer receive Jellyfin administrator permissions.
This is why I strongly recommend keeping a separate local admin account while testing SSO. Don’t make your only Jellyfin administrator depend on an external identity provider and a role mapping you’re still configuring.
Fixing an existing locked-out admin
Credit to Spyros from the comments for this recovery method.
If you’ve already configured OIDC and your normal Jellyfin account has lost administrator access, the plugin configuration can be edited directly.
On my Docker setup the configuration was under:
/jellyfin/data/plugins/configurations/SSO-Auth.xmlYour actual host path may differ depending on where the Jellyfin /config volume is mounted. The important part is the Jellyfin plugin configuration file:
plugins/configurations/SSO-Auth.xmlFind the <AdminRoles> section and make sure it contains the exact Authentik group that should grant administrator access.
<AdminRoles>
  <string>authentik Admins</string>
</AdminRoles>Or, if you’ve created a dedicated Jellyfin administrator group:
<AdminRoles>
  <string>jellyfin-admins</string>
</AdminRoles>Save the file and restart Jellyfin.
After logging in again through Authentik, the account should regain Jellyfin administrator rights as long as the configured group is present in the incoming role claim.
If it still doesn’t work
Don’t just keep changing AdminRoles randomly. First confirm what Authentik is actually sending.
- Confirm the Jellyfin plugin’s Role Claim is set to the claim containing your groups — commonly
groupswith Authentik. - Confirm the exact Authentik group name matches the value entered in Admin Roles, including spaces and capitalisation.
- Confirm the user is actually a member of that Authentik group.
- Check the Jellyfin logs during an SSO login for role/claim errors.
- Keep your local break-glass admin available until the SSO mapping has been tested successfully.
Official LDAP vs community OIDC
As of August 2026 there are effectively two Authentik/Jellyfin paths:
- LDAP: the method currently documented by Authentik. It uses Authentik’s LDAP provider/outpost plus Jellyfin’s LDAP Authentication plugin.
- OIDC: the community SSO-plugin method covered by this article. The old 9p4 project is archived; the Flowfin revival is the current continuation but is not yet a stable release.
I still prefer OIDC conceptually for browser SSO, so I’m keeping this article rather than archiving it completely. Just be aware that it is now a community-plugin path, not Authentik’s current official Jellyfin integration.
References
- Current Authentik Jellyfin integration — LDAP
- Flowfin Community SSO for Jellyfin
- Archived 9p4 Jellyfin SSO plugin
- Jellyfin plugin repositories/documentation
And seriously — keep that second local admin until you’ve proved the OIDC role mapping works. Saving five minutes during setup isn’t worth locking yourself out of your own Jellyfin server 😅
thank you a lot for your instructions.
In case you already did the booboo and you are locked out (if you haven’t created a second user), find the jellyfin file `plugins/configurations/SSO-Auth.xml` and edit it. in Adminroles XML line, replace it with
authentik Admins
Save, exit edit, and restart jellyfin.
refresh page and you should have back the admin rights.
thats awesome, thanks for this.
I’ll add this in with credit when work slows down a little 🙂